Identity and Access Management is rarely a tooling problem
Most IAM failures aren’t caused by weak technology. They fail because of poor decisions, unclear ownership, unrealistic delivery models, and a lack of experienced judgement at the points where it matters most. Arcalis Services exists to address those failures.
One practice.
One senior practitioner.
Arcalis is deliberately structured differently from traditional consultancies.
There are no delivery teams, junior analysts, or account layers. Every engagement is led and delivered end‑to‑end by the founding practitioner.
This model exists for one reason: to reduce risk.
IAM programmes accumulate risk fastest at hand‑off points — between strategy and delivery, between design and implementation, and between advisory guidance and real‑world constraints. Removing those hand‑offs significantly reduces architectural erosion, rework, and control failure.
Clients work directly with the person accountable for decisions, outcomes, and advice — from initial scoping through to final delivery.
Led by experience, not process
Arcalis is founded and led by Andrew Cant CITP FBCS, a senior IAM and cybersecurity consultant with:
- 25 years in enterprise IT and security
- Over a decade specialising in IAM delivery, architecture, and advisory
- Board‑level and executive advisory experience
- Deep exposure to regulated and security‑critical environments
Andrew’s background spans the full IAM lifecycle — from strategy and operating model design, through platform selection and delivery oversight, to programme rescue and post‑incident remediation.
This is not theoretical IAM. It is experience gained where failure is visible and consequences are real.

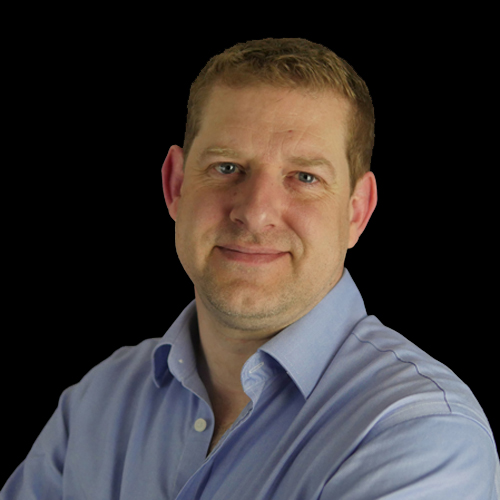
Senior Accountability
Andrew Cant acts as design authority, risk advisor, and escalation point on every Arcalis engagement. All strategic, architectural, and governance decisions are made or reviewed directly by him, ensuring continuity of judgement and clear accountability from start to finish.
Adversary‑tested identity security
In 2021, Arcalis led the defence and remediation of a state‑sponsored intrusion (APT29) targeting enterprise infrastructure. That experience fundamentally shapes how identity security is approached:
- Controls are assessed for how they fail under pressure — not how they appear in policy
- Privileged access, identity governance, and authentication are treated as attack surfaces
- Risk is evaluated through adversary behaviour, not platform checklists
This directly informs Arcalis’ work in identity security, risk reduction, and IAM programme assurance.
Independent by design
Arcalis has no vendor affiliations, resale agreements, or delivery quotas.
That independence enables:
- Objective architectural decisions
- Honest risk assessments — even when uncomfortable
- Platform‑agnostic advice driven by context, threat, and regulation
- The freedom to recommend slower, safer approaches when required
Clients receive recommendations shaped solely by what reduces identity risk — not by partner commitments or roadmap alignment.
Where Arcalis is most effective
Arcalis works best with organisations that recognise IAM as a strategic security discipline, not an IT side‑project.
Typically, these organisations are:
- Mid‑market enterprises with genuine IAM complexity
- Operating in regulated or high‑trust sectors
- Managing cloud, hybrid, or modern identity environments
- Facing regulatory scrutiny, audit exposure, or executive accountability
- Running IAM programmes that are stalled, over‑promised, or drifting into risk
If your IAM challenges require senior judgement rather than scale, Arcalis is intentionally structured for that work.
How Arcalis Approaches Identity Risk
We treat identity and access management as a primary risk control, not a supporting security function. Identity decisions influence breach impact, regulatory outcomes, audit confidence, and executive accountability - often more than perimeter or endpoint controls.
Our approach focuses on identifying where identity failures would carry the greatest consequence, and ensuring controls are designed to hold under operational, organisational, and adversarial pressure. This means prioritising judgement, clarity of ownership, and defensible decision‑making over theoretical completeness.
For senior leaders, this results in an IAM posture they can explain, justify, and stand behind - to auditors, regulators, boards, and incident responders alike.
How this connects to our services
The Arcalis delivery model directly underpins our service offerings:
- IAM Strategy & Architecture — grounded in real delivery constraints
- Identity Security & Risk Reduction — informed by adversary behaviour
- IAM Programme Rescue & Assurance — focused on restoring control and credibility
- Cloud & Modern Platform IAM — designed for operational reality
- Regulatory, Audit & Compliance IAM — evidence‑led and defensible
- Senior Advisory & Fractional IAM Leadership — experienced leadership without permanent overhead
The same senior practitioner underpins every service — ensuring continuity, accountability, and sound decision‑making.
A direct conversation
If you are carrying identity risk you cannot easily quantify, if your IAM programme feels fragile despite investment, or if you need experienced IAM leadership without building a team —
Arcalis offers a direct, senior‑level conversation focused on outcomes, not sales.