IAM Incident & Crisis Response
Calm, identity-led support when security incidents expose critical weaknesses

When identity controls are bypassed or fail, rapid containment and informed decision‑making matter more than tooling.
When organisations experience a cyber incident, identity and access controls are often at the centre of what failed — even if they weren’t initially suspected.
Arcalis provides experienced, independent IAM leadership during and after security incidents, helping organisations stabilise, understand what went wrong, and put the right identity controls in place to prevent recurrence.
When Identity Becomes the Issue
Following a security incident, organisations often discover that identity controls were bypassed, misconfigured, or inconsistently applied — enabling attackers to escalate access and move laterally.
In these moments, organisations don’t need generic incident response. They need experienced identity specialists who can assess IAM failure points, advise on containment and recovery priorities, and guide decision‑making under pressure.
What We Do in a Crisis
Strategy and Architecture Grounded in Reality
Our focus during an incident is not tool deployment or long‑term redesign, but providing immediate, identity‑led clarity that supports containment, recovery, and executive decision‑making.
- Rapid identification of IAM control failures contributing to the incident • Advisory input into access containment and privilege reduction
- Assessment of identity attack paths and architectural weaknesses
- Guidance for security, incident response, and executive teams
- Clear recommendations for immediate remediation and stabilisation
IAM Advisory Under Pressure
When identity failures surface during incidents, organisations do not need generic response playbooks or accelerated tool deployment. They need clear, calm IAM judgement grounded in how identity behaves under attack.
Arcalis provides senior identity advisory support during and immediately after security incidents - helping organisations understand how IAM contributed to impact, where controls failed or were bypassed, and which corrective actions genuinely reduce recurrence risk.
Our role is not to direct incident response teams, but to provide identity‑specific clarity that supports executive decision‑making, stabilisation efforts, and defensible post‑incident remediation.
What we Mean by Threat‑Informed IAM
At Arcalis, threat‑informed IAM means designing and governing identity controls based on how capable adversaries actually compromise environments — not how policies, frameworks, or vendor diagrams assume they should behave.
Rather than starting with tooling or theoretical best practice, we begin with real attack paths: how identity is abused during intrusions, how privilege is escalated, how controls fail under pressure, and where organisations consistently underestimate risk.
This approach is informed by direct experience defending complex environments during live security incidents, including nation‑state intrusion activity. It shapes how we assess IAM maturity, define architectures, prioritise controls, and advise decision‑makers — ensuring that identity controls remain effective when they matter most, not just when audited.
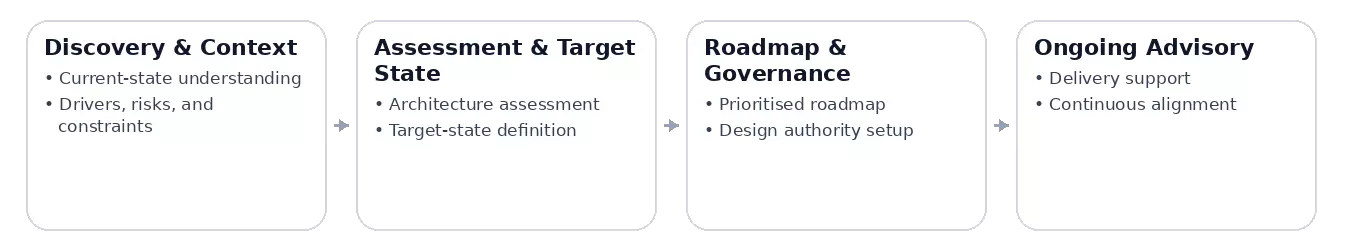
How We Engage During an Incident
Our incident engagements are designed to be calm, focused, and proportionate — providing the right level of support without adding noise or disruption.
From Crisis Response to Stability and Confidence
Once immediate risks are understood and controlled, organisations often recognise the need for ongoing IAM leadership to ensure weaknesses are properly addressed and not re‑introduced.
Many of our crisis engagements evolve into retained advisory support, where we continue to provide:
- Ongoing IAM risk oversight
- Architecture correction and stabilisation
- Design authority and delivery assurance
- Board‑level and regulatory confidence
Why Arcalis in Crisis Situations
Arcalis is an independent IAM consultancy with deep experience supporting organisations where identity failures have real security, operational, and regulatory consequences.
We understand how IAM behaves under attack — and how poor identity decisions made in a crisis can create long‑term risk.
- Deep, specialist IAM expertise
- Calm, senior advisory presence
- Independent and tool‑agnostic
- Proven experience in complex and regulated environments
- Focused on sustained improvement, not just incident closure
Start a conversation
If you are dealing with an identity‑related security incident — or are concerned that IAM weaknesses may have contributed — we’re happy to talk.
No sales pitch. Just experienced, identity‑focused advice when it matters.